PlugLeak
Find leaked keys in your AI-built app in 20 seconds
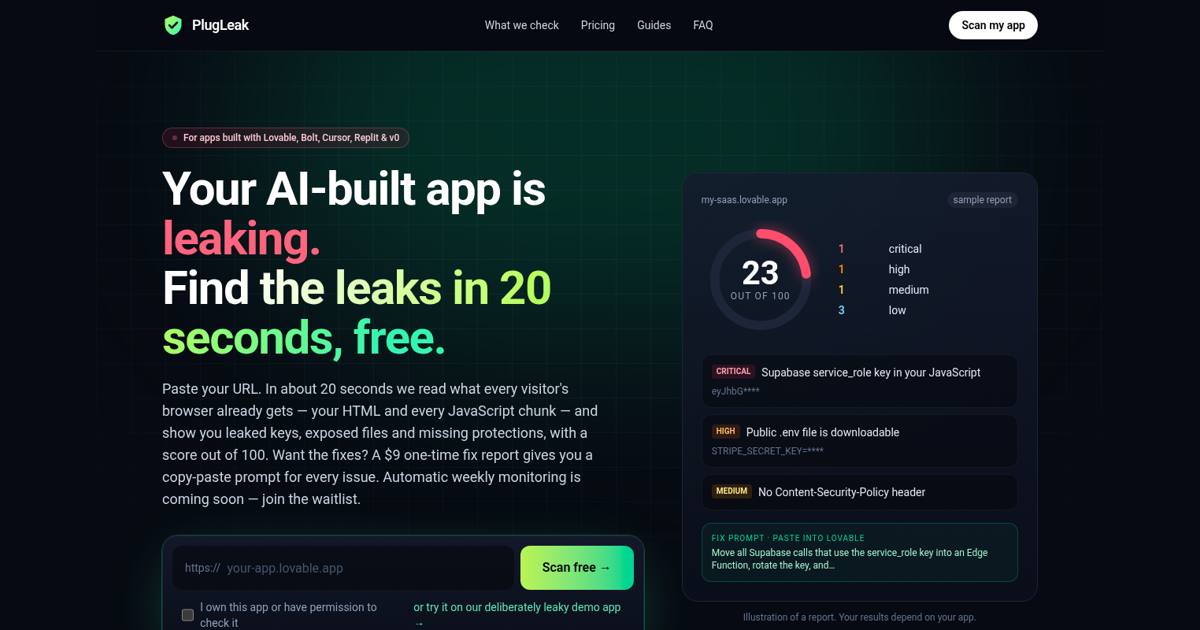
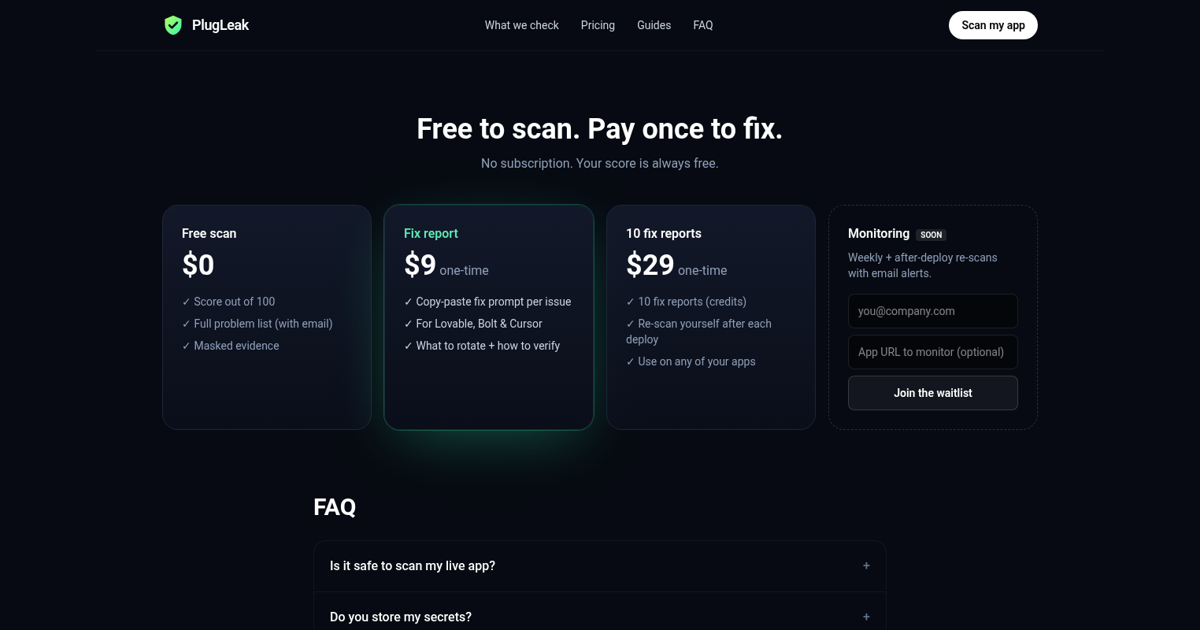
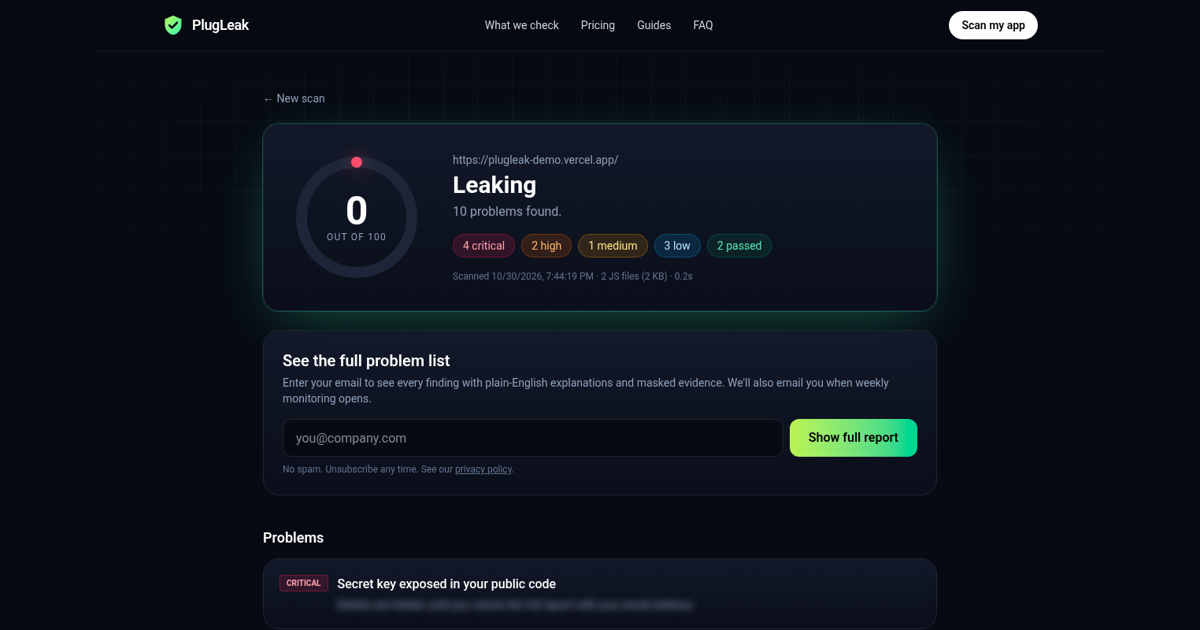
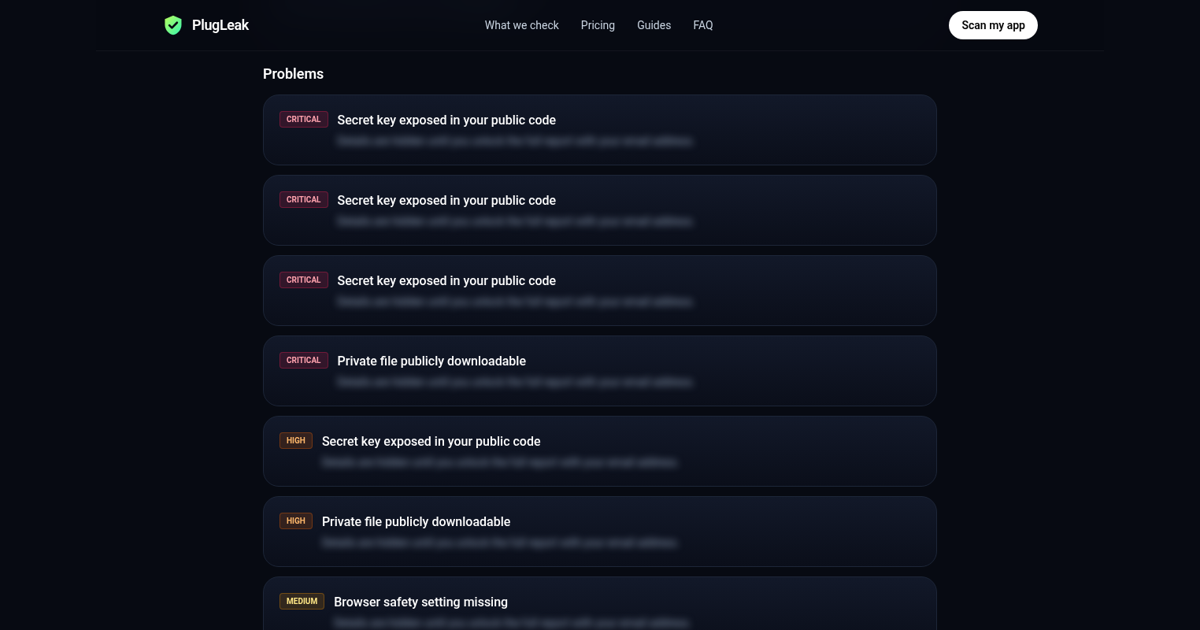
PlugLeak is a free, passive security check for apps built with Lovable, Bolt, Cursor and Supabase. Paste your URL, get a score out of 100 in ~20 seconds, plus leaked API keys, public .env/.git and header/SSL issues. GET requests only; secrets masked. Automated check, not an audit. Scan is free; $9 one-time Fix Report (or $29 for 10) adds paste-ready fix prompts.
Features
Scans HTML and all JS chunks for leaked keys
Detects Supabase service_role JWTs
Checks /.env and /.git exposure
Headers, HTTPS and SSL expiry checks
Score out of 100 with shareable report
Paste-ready fix prompts for Lovable/Bolt/Cursor
Use Cases
Check an AI-built app before launch
Verify no secrets leaked after a deploy
Get copy-paste fixes for your AI coding tool
Comments


PlugLeak's free scan plus $9 fix report is a clever upsell, especially for Lovable and Bolt users rushing to launch. Does the score out of 100 actually catch a leaked Supabase servicerole JWT before it gets abused, or is it more of a carta natal https://micartanatal.org -style novelty check?
Premium Products

















































Makers
Makers
Comments
PlugLeak's free scan plus $9 fix report is a clever upsell, especially for Lovable and Bolt users rushing to launch. Does the score out of 100 actually catch a leaked Supabase servicerole JWT before it gets abused, or is it more of a carta natal https://micartanatal.org -style novelty check?
Premium Products
New to Fazier?

Find your next favorite product or submit your own. Made by @FalakDigital.
Copyright ©2026. All Rights Reserved